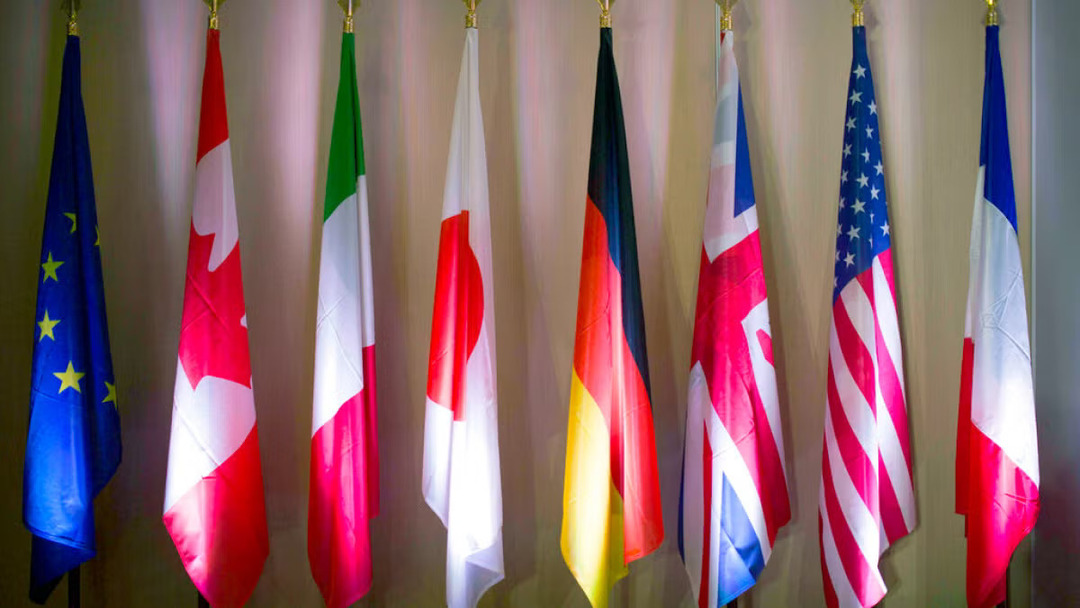
G7 AI safety talks are no longer just a government conversation about abstract risks. With executives from major AI companies expected around the summit table, the debate is shifting toward a harder question: how much influence should frontier AI builders have over the global rules meant to restrain them?
That tension matters because AI safety is moving from company policy to diplomatic coordination. The same pressure behind Washington’s new AI test is now expanding globally, where model release, online safety, cyber misuse, and platform accountability are becoming shared concerns among major economies.
G7 AI Safety Talks Are About Power, Not Just Policy
The G7 has already treated AI as more than a consumer technology issue. The latest summit focus pushes that further by bringing major AI companies into discussions that sit closer to security, public trust, and economic stability.
That is the real story. Governments need the technical cooperation of firms building the most capable models. Those companies understand model behavior, deployment limits, infrastructure constraints, and abuse patterns better than most policymakers. But the same companies also have commercial incentives to shape rules that affect release speed, compliance cost, and global market access.
This creates a delicate balance. Governance needs expertise, but it cannot become rulemaking by the companies being governed.
AI Companies Are Becoming Geopolitical Actors
Anthropic, OpenAI, Google, and Mistral AI are not traditional defense contractors or telecom operators, yet their systems increasingly touch national priorities. Their models can affect cybersecurity, online information flows, software development, education, enterprise automation, and government services.
That is why the upcoming G7 summit matters beyond the guest list. When AI executives enter a leaders’ summit environment, they are no longer just product builders. They become participants in a global policy conversation about infrastructure, safety, and public risk.
The shift is especially important for smaller and open-model players. Mistral AI’s presence reflects Europe’s interest in keeping AI governance from becoming a U.S.-only platform conversation. Google and OpenAI bring scale. Anthropic brings safety positioning. Together, they show how the AI policy table now includes both governments and companies with global technical leverage.
Online Safety Is Becoming an AI Infrastructure Issue
Online safety used to be framed mainly around platforms: moderation, harassment, child safety, scams, extremism, and misinformation. AI changes the mechanics.
Generative systems can create synthetic media, automate persuasion, scale spam, imitate trusted voices, and assist coordinated manipulation. Even when the model is not designed for harm, its outputs can be used inside larger abuse pipelines.
That makes AI safety an infrastructure question. The issue is not only what one chatbot says. It is how models connect to social platforms, search, messaging apps, image tools, coding systems, and agent workflows.
The G7 already has a foundation for this debate through the Hiroshima AI Process code, which created voluntary principles for organizations developing advanced AI systems. The current challenge is turning broad principles into practical expectations that can survive real product cycles.
Voluntary rules need proof when models are deployed at global scale.
The Hardest Problem Is Accountability Across Borders
A frontier AI model can be trained in one country, hosted in another, accessed globally, and used in a third jurisdiction for harm. That makes national regulation alone incomplete.
The G7 can help align expectations among major economies, but alignment is not the same as enforcement. Companies may face different rules across the United States, the European Union, the United Kingdom, Japan, and Canada. Governments may agree on safety language while disagreeing on liability, model transparency, open-source releases, or national-security access.
The table below shows why the summit conversation is likely to matter beyond headlines.
| Policy Pressure Point | Why It Matters | Hard Question |
|---|---|---|
| Model safety testing | Helps identify dangerous capabilities before release | Who defines a serious test? |
| Online safety | AI can scale scams, synthetic media, and manipulation | Who is responsible after deployment? |
| Cyber misuse | Models can assist attackers and defenders | How much testing should be required? |
| Company transparency | Builds trust around model behavior and safeguards | What must stay confidential? |
| Global coordination | Reduces conflicting national rules | How much authority should the G7 have? |
The table shows the underlying challenge: AI safety is not one problem. It is a stack of technical, legal, commercial, and geopolitical decisions.
The Risk Is a Safety Conversation That Moves Too Slowly
AI development moves faster than diplomacy. That mismatch may be the biggest weakness in global governance.
Summits can create statements, voluntary commitments, and working groups. AI companies can ship new capabilities faster than most international processes can respond. The danger is not that G7 talks are useless. The danger is that they create the appearance of control without mechanisms that keep pace with deployment.
This is where speed becomes risk. If governments wait for perfect alignment, companies may set the practical norms by default. If governments move too aggressively without technical grounding, they may create rules that are easy to announce and hard to implement.
The strongest outcome would be neither symbolic cooperation nor heavy-handed overreach. It would be a repeatable process for model evaluation, incident sharing, abuse monitoring, and coordinated response when powerful systems create cross-border harm.
The Next Signal Is Whether CEOs Accept Real Constraints
The next phase will show whether G7 AI safety talks produce meaningful pressure or just polite alignment.
The first signal is whether companies accept clearer expectations for model testing before major releases. The second is whether online safety commitments include measurable obligations around synthetic media, abuse prevention, and platform integration. The third is whether governments can coordinate without letting companies define every technical threshold.
The fourth signal is whether the G7 treats AI safety as part of broader security infrastructure. That would connect model governance to cyber defense, critical systems, public information integrity, and supply-chain resilience.
G7 AI safety talks matter because frontier AI has outgrown the idea that companies can govern themselves through product policy alone. The firms building these systems need a seat at the table because their technical knowledge is essential. But governments must prove that the table has rules, consequences, and public accountability. Otherwise, the global AI safety debate risks becoming a stage where the most powerful builders help write the guardrails while still holding the keys.
FAQ
Why are AI executives attending G7 safety discussions?
AI executives bring technical knowledge about model behavior, deployment risk, and abuse patterns. Governments need that expertise, but they also need safeguards so companies do not dominate the rules.
What does online safety have to do with AI?
AI can scale synthetic media, scams, impersonation, spam, and coordinated manipulation. That makes online safety harder because harmful content can be produced faster and more cheaply.
Why do G7 AI safety talks matter?
They matter because frontier AI risks cross borders. A model released in one country can affect users, platforms, cyber systems, and public trust across many jurisdictions.